CRITICAL PATCH · NGINX · NGINX2ROOT · CHECKED 09:00 ASIA/GAZA, 21 NOV 2026
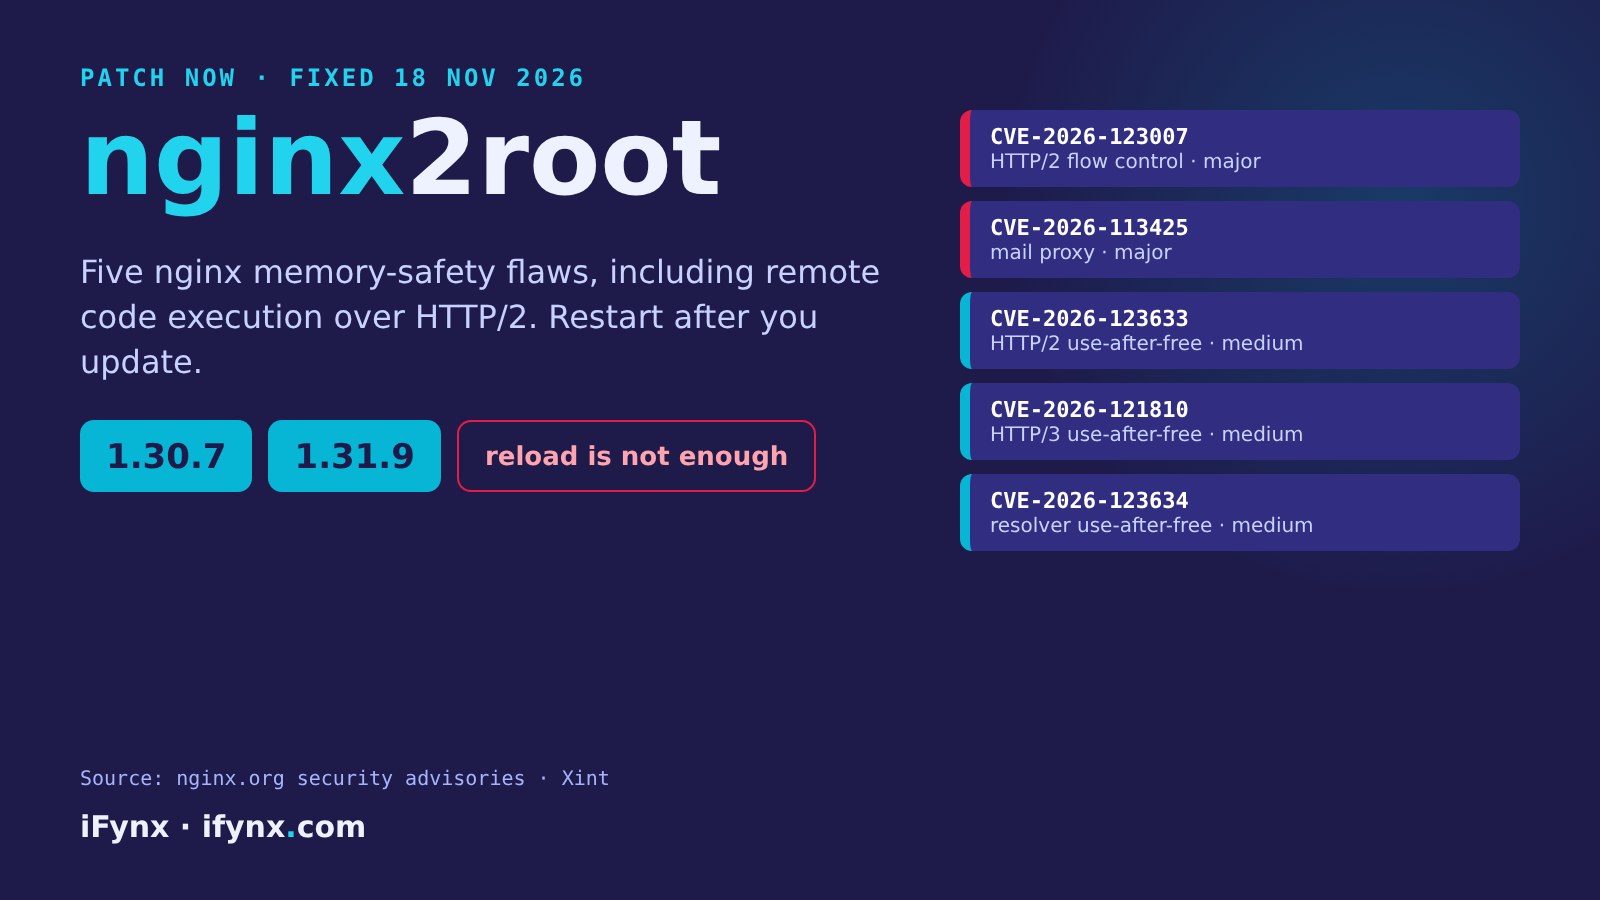
Update nginx to 1.30.7 or 1.31.9 now. On 18 November 2026 nginx fixed five memory-safety flaws, nicknamed nginx2root, the worst of which (CVE-2026-123007) can let a remote attacker run code on servers with HTTP/2 enabled. No attacks are reported yet, but the researchers say they have working exploits.
Primary sources: nginx.org security advisories and the Xint research write-up. A reload is not enough: restart nginx fully after upgrading.
At iFynx we build and run websites, APIs and platforms for banks, fintechs, retailers and government-facing teams in the UAE, Saudi Arabia, Egypt and Palestine, and nginx sits in front of most of them. It is likely in your stack too, even if nobody on the team installed it on purpose: in Kubernetes ingress, API gateways and container images. Here is what was fixed, which settings matter, and the order to fix things in.
Which nginx versions are affected by nginx2root?
All five bugs are fixed in nginx 1.30.7 (stable) and 1.31.9 (mainline), both released on 18 November 2026, according to nginx.org. Each bug only matters if a specific feature is switched on, so the table below shows what each needs.
| CVE | What it is | nginx severity | Needs | Vulnerable versions |
|---|---|---|---|---|
| CVE-2026-123007 | Memory corruption in HTTP/2 flow control | major | HTTP/2 enabled | 1.9.5 to 1.31.8 |
| CVE-2026-113425 | Use-after-free in the mail proxy module | major | mail proxy with auth_http | 0.5.33 to 1.31.8 |
| CVE-2026-123633 | Use-after-free in HTTP/2 | medium | HTTP/2 + requests sent to an upstream | 1.19.7 to 1.31.8 |
| CVE-2026-121810 | Use-after-free in HTTP/3 | medium | HTTP/3 (QUIC) + upstream | 1.25.0 to 1.31.8 |
| CVE-2026-123634 | Use-after-free in the resolver | medium | resolver + variable proxy_pass + mirror | 0.6.18 to 1.31.8 |
STABLE
1.30.7
Released 18 Nov 2026
MAINLINE
1.31.9
Released 18 Nov 2026
DISTRO PACKAGES
Check the notice
The fix may be backported under an older version number
Security Affairs reports that all five have a CVSS 4.0 score of 9.2 and that NGINX Plus is fixed in 37.3.0.1 and 37.0.8.1. We could not read F5’s advisory pages to confirm those two points, so treat them as reported, not confirmed. Which CVSS number applies matters less than the fact that the fix is out.
How bad is CVE-2026-123007, and what does “to root” mean?
CVE-2026-123007 is a memory corruption bug in how nginx keeps track of HTTP/2 flow control. Xint says it can be triggered remotely without a login on servers with HTTP/2 on, and can lead to code running as the nginx worker process. That user normally has limited rights. The “root” part came from chaining it with a separate Linux kernel flaw, which in the researchers’ demos also escaped a Docker container. We describe this only at a high level; no attack steps here.
Remote request
HTTP/2 traffic hits a vulnerable nginx
nginx worker
Code runs as the worker user (CVE-2026-123007)
Kernel flaw
A separate Linux bug turns that into root
Source: Xint. The kernel flaw is separate from nginx; patching either breaks this chain, patching both is the goal.
Is anyone exploiting this? As of 21 November 2026 we found no report of attacks, and CVE-2026-123007 was not on CISA’s KEV list when Security Affairs checked. But the researchers published videos of working exploits on AWS, Google Cloud, Azure and bare metal, and nginx runs a huge share of the web. Expect attackers to try.
nginx2root fix checklist for Gulf and Egypt teams
Do these in order
nginx -v prints.http2 off; on 1.25.1+, or remove http2 from listen). This does not cover the HTTP/3, resolver or mail-proxy bugs: switch off QUIC listeners you don’t need, avoid request-time DNS in proxy_pass, and limit the mail proxy to trusted networks.Why this matters in the UAE, Saudi Arabia and Egypt
Bank portals, payment gateways, e-commerce sites and government e-services in the region are commonly served through nginx, often inside Kubernetes ingress controllers or vendor appliances that teams forget to update. Two traps we see often: sites behind Cloudflare or another CDN assume they are covered, but the origin nginx still runs the vulnerable code; and container images keep an old nginx long after the host is patched. This is the second HTTP/2 server flaw this week after Apache HTTP Server CVE-2026-119618: exploited mod_http2 RCE, so check both web servers together.
How iFynx can help
iFynx builds and runs bilingual (Arabic and English) web platforms for the UAE, Saudi Arabia, Egypt and Palestine. We can:
- Find every nginx in your servers, containers and Kubernetes ingress
- Plan and run the upgrade and full restart with minimal downtime
- Harden nginx and kernel settings, and set up alerts for worker crashes
Frequently asked questions
What is nginx2root?
nginx2root is the name researchers at Xint gave to five memory-safety flaws in nginx, fixed on 18 November 2026: CVE-2026-123007, CVE-2026-113425, CVE-2026-123633, CVE-2026-121810 and CVE-2026-123634. nginx rates two of them major and three medium. The name comes from the researchers’ demo that chained one of them with a Linux kernel flaw to get root.
Which nginx version fixes nginx2root?
nginx 1.30.7 (stable) and 1.31.9 (mainline), released on 18 November 2026, fix all five. Distribution packages may carry the fix under an older version number, so check your distribution’s security notice.
Is my server vulnerable if I don’t use HTTP/2?
Possibly not to the most serious bug, CVE-2026-123007, which needs HTTP/2. But the other four depend on HTTP/3, the mail proxy or certain resolver and mirror setups, so check each one against your configuration, or simply upgrade.
Are these flaws exploited in the wild?
As of 21 November 2026, we found no report of attacks, and Security Affairs reported that CVE-2026-123007 was not in CISA’s Known Exploited Vulnerabilities catalog when it wrote its story. The researchers say they have working exploits but deliberately left out the final steps. With the patch public, that can change quickly.
Do sites behind Cloudflare or a CDN still need to patch?
Yes. A CDN in front changes which traffic reaches your server, but the origin nginx still runs the vulnerable code, and many internal services and ingress controllers are reachable without the CDN. Patch the origin.
How can iFynx help?
iFynx builds and runs web platforms for teams in the UAE, Saudi Arabia, Egypt and Palestine. We can find every nginx instance in your stack, plan a safe upgrade and restart, and harden the configuration.
Sources
- nginx.org security advisories (lists all five CVEs, severity and versions)
- nginx.org CHANGES: nginx 1.31.9, 18 Nov 2026
- Xint: nginx2root remote code execution write-up (18 Nov 2026)
- Security Affairs: nginx2root (19 Nov 2026)
- BleepingComputer: critical nginx2root bugs
Related reading
Every Sunday: the most serious confirmed CVEs and breaches, who is exposed in Saudi Arabia, the UAE and Egypt, and what to patch first. Free, in English and Arabic, one-click unsubscribe.
✓ You’re subscribed. A welcome email is on its way; the first issue arrives on Sunday.