Update 19 Nov 2026, 01:05 Asia/Gaza: still unconfirmed, and a supplier link.
Nvidia has still not confirmed a breach, and the group has still published no samples. Ransomnews notes that The Gentlemen listed Jentech, a Taiwanese maker of cooling parts that calls itself an Nvidia MGX ecosystem partner, on 6 October 2026, claiming 9 TB of data (also unverified). That raises the possibility that any “Nvidia” data comes from a supplier rather than Nvidia’s own systems. Nobody has confirmed this. The timer runs out on the morning of 28 November (UTC).
UNCONFIRMED CLAIM · NVIDIA · THE GENTLEMEN · CHECKED 19:00 ASIA/GAZA, 18 NOV 2026
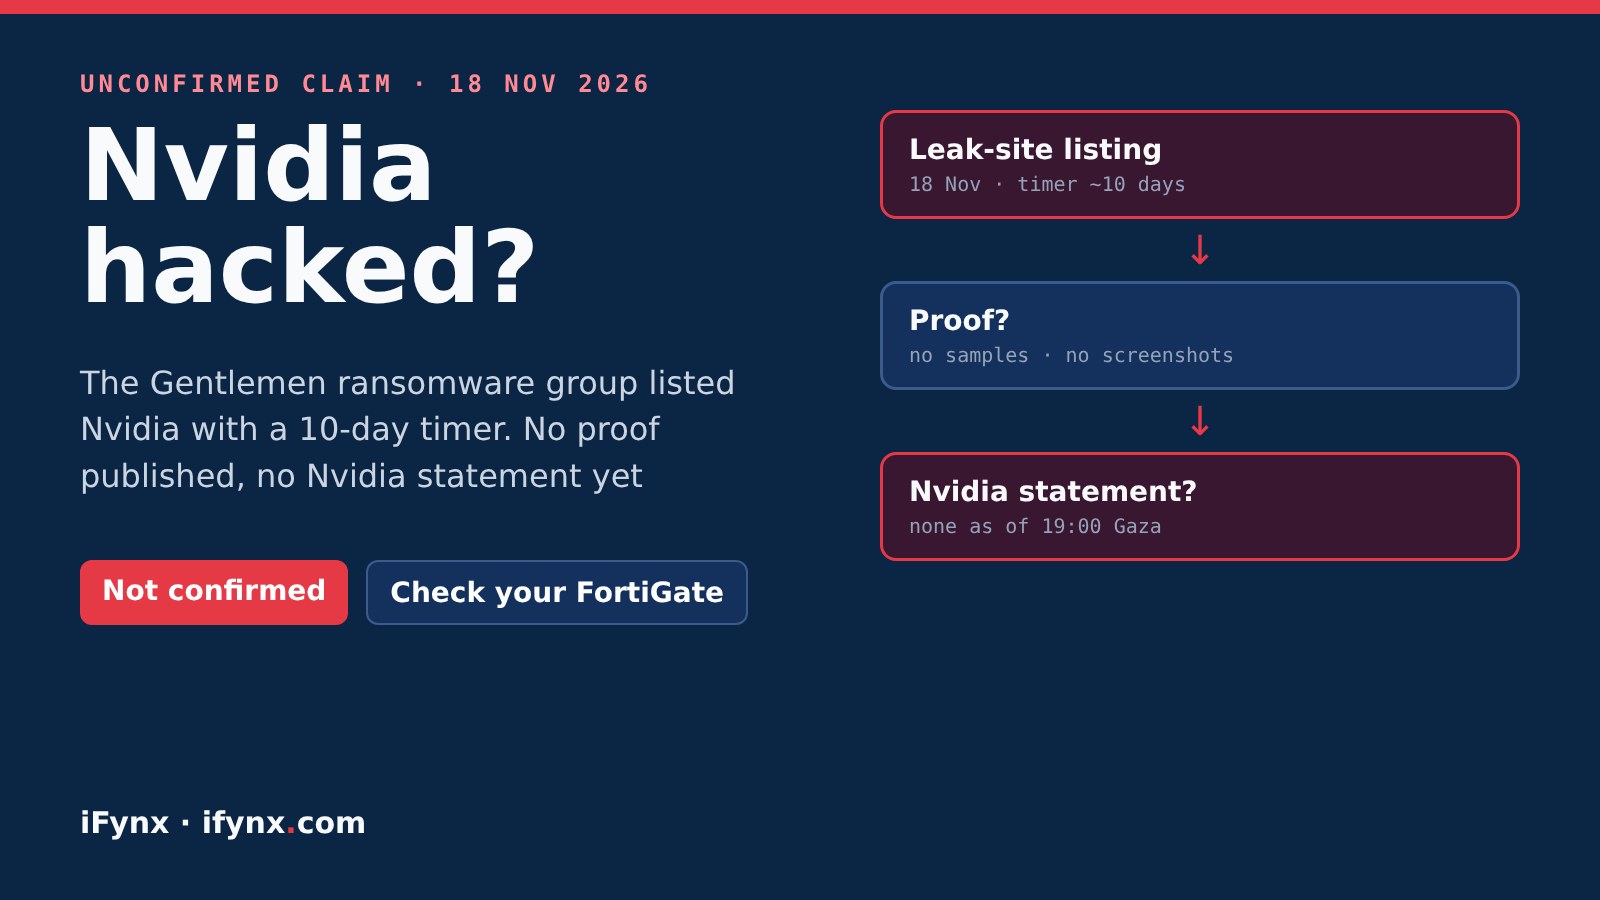
Was Nvidia hacked? Not confirmed. The ransomware group The Gentlemen listed Nvidia on its extortion site on 18 November 2026 and set a timer of about 10 days, but it has published no stolen files, and Nvidia has neither confirmed a breach nor commented. Treat it as an unverified claim for now.
Sources: Glitchwire, Digit and FortiGuard’s profile of the group. The practical lesson for companies in the Gulf and Egypt is below: how this group usually gets in, and how to close those doors.
At iFynx we build and secure platforms for banks, fintechs and government-facing teams in the UAE, Saudi Arabia, Egypt and Palestine. “Nvidia hacked” is spreading fast on social media today, so here is what is actually known, what is not, and why the group behind the claim matters more to your company than Nvidia’s own story.
Nvidia ransomware claim: what we know
| Point | What we know |
|---|---|
| Claim | The Gentlemen ransomware group listed Nvidia on its extortion site on 18 Nov 2026 |
| Timer | About 10 days (around 28 Nov 2026) before an alleged data release |
| Proof | None published so far: no sample files, no internal screenshots |
| Nvidia | No confirmation and no public comment as of 19:00 Gaza, 18 Nov |
| Trackers | Ransomware.live and Breach House logged the claim as ‘pending’ |
| The group | Ransomware since mid-2025, double extortion, targets Windows, Linux and ESXi |
| Usual entry | Stolen credentials, VPN and RDP abuse, unpatched edge devices incl. FortiOS CVE-2024-55591 |
| Status | UNCONFIRMED claim |
Unconfirmed: ransomware groups sometimes list companies they never breached, or re-use data from old incidents or from a supplier. Until samples appear or Nvidia makes a statement, nobody outside the group can say whether Nvidia’s systems were hit. We will update this page either way.
What happens next
Who are The Gentlemen?
The group appeared in mid-2025 and runs double extortion: steal data, encrypt servers, then threaten to publish. Fortinet’s FortiGuard Labs lists Windows, Linux and VMware ESXi as targets, 22 industries including energy, finance and government, and the Middle East among its regions. Its usual ways in are ordinary: stolen passwords, VPN and RDP abuse, phishing and unpatched internet-facing systems, including the FortiOS authentication bypass CVE-2024-55591. Researchers quoted by Cybernews warn that the group has exaggerated claims and recycled stolen data in the past.
The useful part: check your own edge this week
Whatever is true about Nvidia, the same group hits companies of every size, and FortiGate firewalls and VPNs are everywhere in the UAE, Saudi Arabia and Egypt. Use this checklist:
Edge-device and ransomware checklist
This week’s other supplier and patch stories are worth the same attention: Infoblox breach through a SharePoint migration vendor and Java4Shell: patch order for Gulf and Egypt teams.
How iFynx can help
iFynx builds and secures platforms in Arabic and English for the UAE, Saudi Arabia, Egypt and Palestine. We can:
- Check your firewalls, VPN and remote access for the gaps ransomware groups use
- Set up alerts for mass data transfers and unusual admin tools on servers
- Review and test your backup and restore plan, including virtual machines
Frequently asked questions
Was Nvidia hacked?
Not confirmed. On 18 November 2026 the ransomware group The Gentlemen listed Nvidia on its dark-web extortion site with a countdown of about 10 days. As of 19:00 Gaza time on 18 November no stolen files or screenshots had been published, and Nvidia had not confirmed a breach or commented publicly.
Who are The Gentlemen?
A ransomware group that appeared in mid-2025 and uses double extortion: it steals data, encrypts systems and threatens to publish the data. Fortinet’s FortiGuard lists it as targeting Windows, Linux and VMware ESXi in 22 sectors and in regions including the Middle East. Researchers quoted by Cybernews say the group has exaggerated claims and recycled old data before.
When will the data be leaked?
The listing shows a timer of roughly 10 days from 18 November, which points to about 28 November 2026. Ransomware groups often use these timers to pressure a victim. A timer is not proof that any data exists.
Should Nvidia customers or gamers do anything?
There is nothing confirmed to act on yet. No customer data, drivers or accounts have been reported as affected. Keep drivers updated only from Nvidia’s official site or app, and be wary of emails or downloads that use the breach story as bait.
Why does this matter to companies in the Gulf and Egypt?
The Gentlemen’s usual way in is not exotic: stolen VPN passwords, exposed RDP and unpatched firewalls, including the Fortinet FortiOS flaw CVE-2024-55591. FortiGate firewalls are very common in the UAE, Saudi Arabia and Egypt, so the useful step is to check your own edge devices this week.
Will iFynx update this page?
Yes. If Nvidia makes a statement, or if the group publishes samples or data, we will add a dated update at the top of this page.
Sources
- Glitchwire: The Gentlemen list Nvidia on extortion site, no proof of breach has emerged (18 Nov 2026)
- Digit: Nvidia ransomware claim, hackers threaten to leak data in 10 days (18 Nov 2026)
- Cybernews: Nvidia ransom demand by The Gentlemen
- FortiGuard Labs: The Gentlemen ransomware threat actor profile