Field note · 16 Nov 2026 · sources re-checked 08:50 Asia/Gaza
wfx-loot is a CI secret stealer that an attacker pushed into GitHub repositories from 10 November 2026, using stolen credentials of 4,837 real GitHub accounts. It was not a GitHub bug: the accounts already had write access.
Researchers at Aikido count 61,764 repositories probed and at least 1,835 where the stealer ran and sent secrets out. It takes every GitHub Actions secret, cloud key and AI provider key it can reach, tries to leave backdoors in AWS and Azure, then reverts its commit and deletes the workflow run. If it ran in your repository, treat every secret that job could reach as stolen. GitHub had published no statement on the campaign when we checked.

At iFynx we build and maintain web, mobile and backend products for banks, fintechs, retailers and public services in the UAE, Saudi Arabia, Egypt and Palestine, and nearly all of them ship through CI pipelines that hold production keys. This is a checklist-first article: start with the ten-minute check below, then read how the attack chain works, how to decide whether you were hit, and the CI/CD secret checklist we recommend for Gulf and Egypt teams. We re-read the Aikido, GitGuardian, OX Security, StepSecurity and BleepingComputer reports on 16 November 2026 at about 08:50 Asia/Gaza (06:50 UTC). We do not reproduce the malware or link to it.
The ten-minute check (any repo you can write to)
- Search your organisation for pull requests titled
docs: dependency audit notesand branches namedwfx-docs. One probe means the account that opened it is compromised, even if nothing else followed. - Search commits since 10 November for
ci: refresh build cache,chore: add ci helper,chore: add dependency audit workflow,ci: restoreandci: cleanup. - Look for a root file named
.ci-plus six characters ending in.sh, or a newpostinstallline inpackage.json. - Open the Actions tab of each workflow and look for a missing run number right after one of those commits. A deleted run is often the only trace.
- If you find any of this, go straight to the decision tree and the rotation steps below. Do not just close the pull request.
Key facts, and who measured them
The numbers differ because each team measured something different, at a different time. We list who said what rather than averaging them.
Key facts · checked 16 November 2026
| Figure | What it counts | Source, date |
|---|---|---|
| 12:45 UTC, 10 Nov (14:45 Asia/Gaza) | Start of the mass wave | Aikido, GitGuardian |
| 24 to 29 Oct | Small precursor: 80 payload patches, 7 accounts, 12 repositories | GitGuardian, 13 Nov |
| 4,837 | Hijacked GitHub accounts that opened probe pull requests | Aikido, 12 Nov; OX Security |
| 61,764 | Repositories probed (to 11 Nov) | Aikido |
| 66,001 | Probe pull requests found by GitHub search on 12 Nov | GitGuardian |
| 8,093 | Public repositories with a malicious commit on the default branch | OX Security |
| at least 1,835 | Repositories where the payload ran and secrets were sent out (OX Security counts at least 1,806) | Aikido, BleepingComputer |
| 10,431 | Probe pull requests into repositories the account did not own, reached through collaborator or organisation access | Aikido, OX Security |
| about 50 | Hijacked accounts that can publish packages (npm, Go, Packagist, PyPI, crates) | Aikido |
| 431 (about 20%) | Accounts already compromised in the October GhostAction wave | GitGuardian |
| One route explained | Some tokens were GitHub App tokens left in a .git/config file that Fly.io-deployed apps served publicly; a small number of Fly.io accounts were affected |
Fly.io notice, 12 Nov 22:00 UTC |
| Not confirmed | How most of the 4,837 credentials were stolen; whether private repositories were hit; who is behind it; any GitHub statement | None published as of our check |
Some hijacked accounts belonged to Fortune 100 organisations, the US General Services Administration, the French government, Nextcloud and WebdriverIO, BleepingComputer reported. No organisation in the Gulf or Egypt has been named in the sources, and we do not speculate about victims.
One source of stolen tokens is now public. In a notice posted at 22:00 UTC on 12 November, Fly.io said its own systems were not breached, but that its deploy-from-GitHub process had left a GitHub access token in the .git/config file of the build directory. Some customer apps shipped that whole directory and served it on the public internet, and an unauthorised party collected the tokens and used them in the wfx campaign. Fly.io began revoking every user token issued to its GitHub App; on 13 November it added that GitHub support had acknowledged the revocation “started and then stopped partway through” and was looking into it. This explains a small number of accounts, not all 4,837.
How the attack chain works
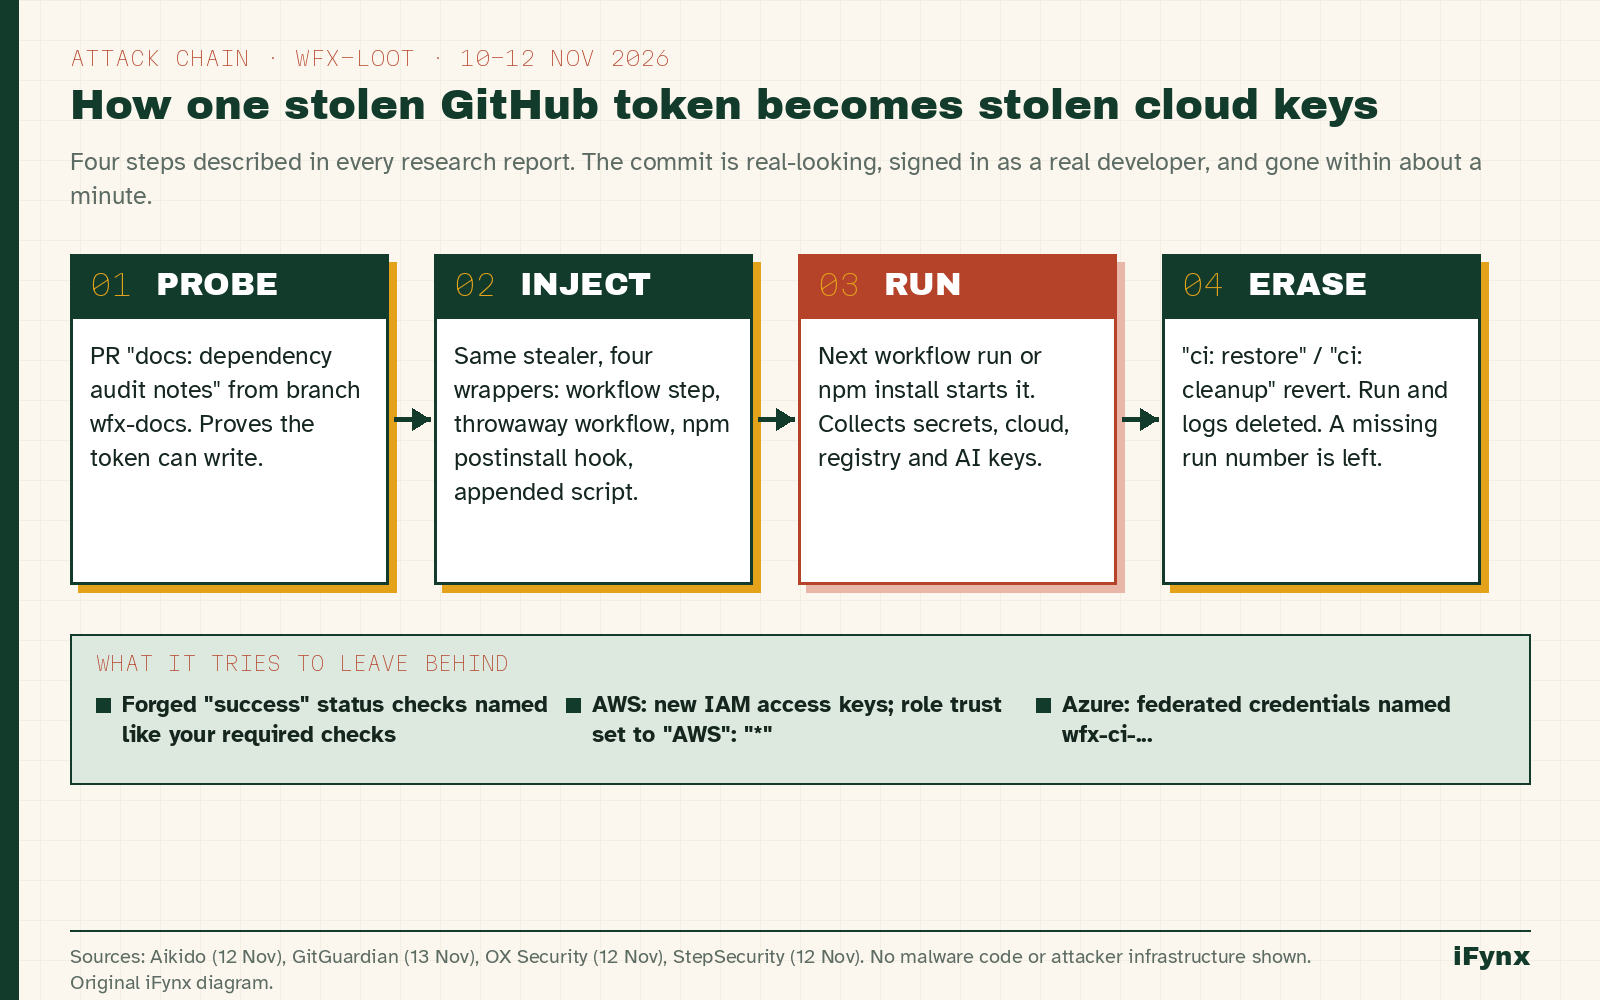
Every report describes the same four steps. The attacker logs in with a stolen token, so every commit appears under a real developer’s name.
- Probe. A harmless-looking pull request titled
docs: dependency audit notes, from awfx-docsbranch, adds one Markdown file. It only proves the token can write to the repository. - Inject. The same stealer, a plain shell script of about 1,300 to 1,500 lines depending on the version, arrives in one of four wrappers: added to an existing workflow as a step called “Restore cache”, as a throwaway workflow on a
chore/branch, as a hidden.ci-script started by an npmpostinstallhook, or appended to an existing script such asdeploy.sh. - Run. The next workflow run, or the next
npm install, starts the stealer. - Erase. The commit is reverted, usually within a minute, with
ci: restoreorci: cleanup, and the workflow run and its logs are deleted.
The script is not obfuscated. OX Security makes the point well: hiding the evidence beats hiding the code. A review of the current branch the next morning will usually find nothing.
Why the npm hook mattered
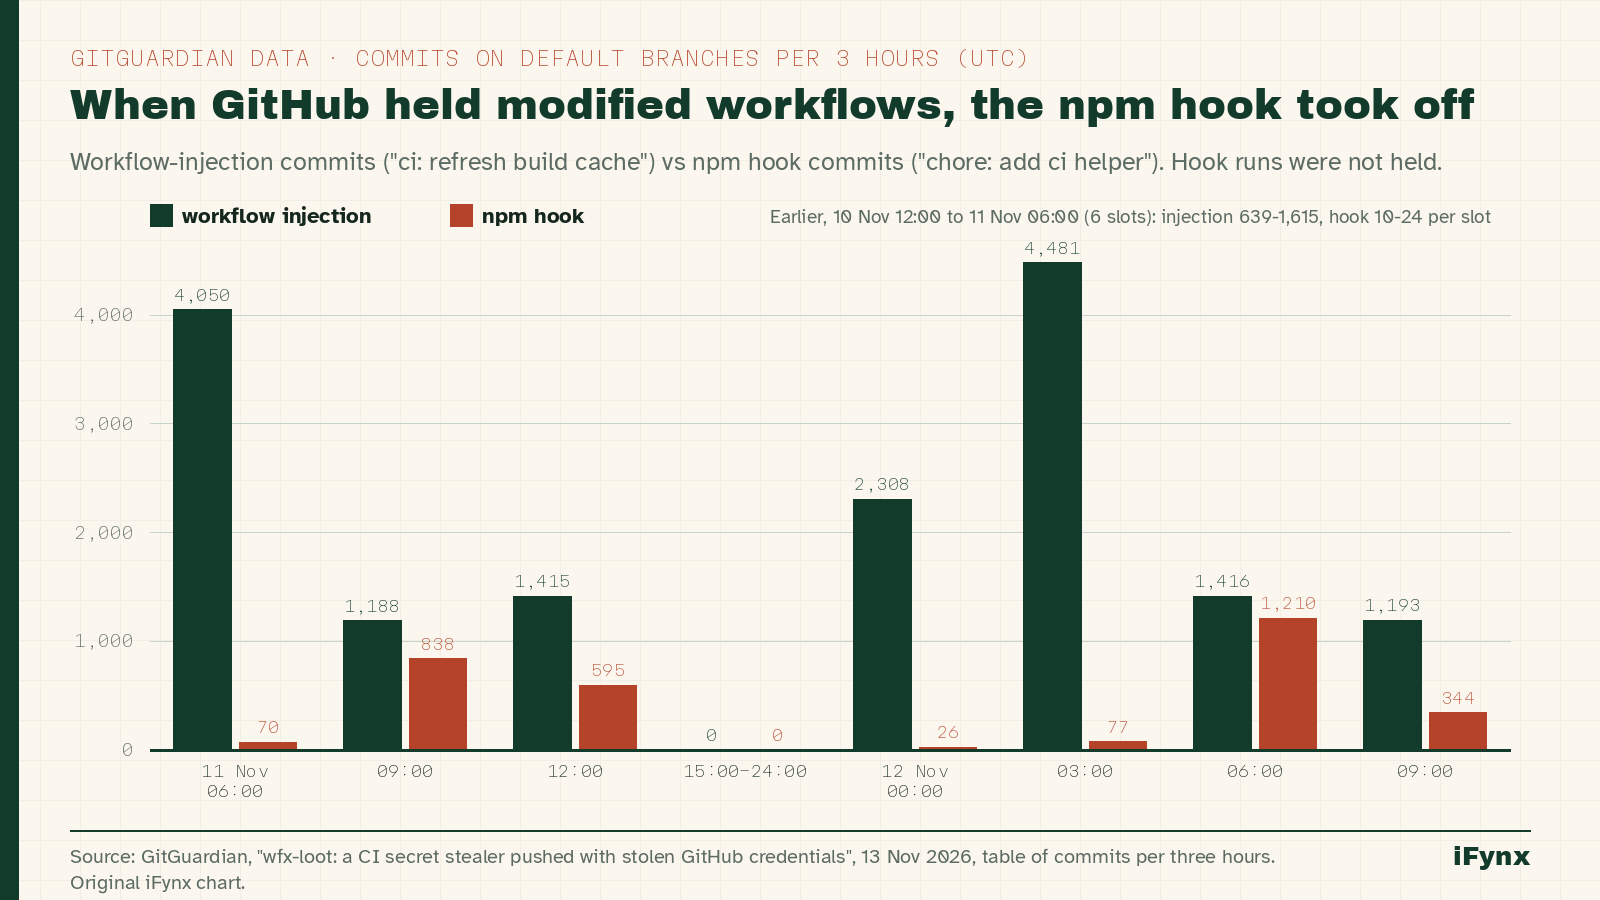
GitGuardian’s analysis adds the most important detail for engineering teams. When the stealer sat inside a workflow file, GitHub held the run: every November payload run GitGuardian could still see ended as action_required and never started. The npm hook form changes no workflow file. The repository’s own trusted workflow runs npm install or npm ci as usual, and npm runs the hidden script. In a sample of 30 repositories that ran jobs on a hook commit, none was blocked; public logs from 19 repositories show the script running, and 18 of them reported a successful delivery.
The attacker noticed. Hook commits went from 10 to 24 per three-hour window on 10 November to 838 on the morning of 11 November and 1,210 on the morning of 12 November. Because the hook also runs outside CI, any developer who ran npm install on an affected repository in that short window may have run the stealer on their own laptop.
What the stealer takes, and what it leaves behind
The stealer collects, in short, everything a CI job can touch:
- every repository and organisation secret and variable, not only the ones the workflow uses, plus the job’s
GITHUB_TOKENand OIDC tokens; - cloud credentials for AWS, Azure and Google Cloud, including instance metadata on self-hosted runners;
- registry and infrastructure credentials: npm, PyPI, Docker, Kubernetes, Vault, Terraform, SSH and GPG keys,
.envfiles and keystores; - AI provider and AI coding-tool keys, including OpenAI, Anthropic, Gemini, Hugging Face, Cursor and GitHub Copilot;
- tokens found in the memory of runner processes, plus up to 60 repository files that match secret patterns and the last 100 commits.
Rotation alone may not be enough, because the script also tries to stay. It posts forged “success” status checks using the names of your required checks, so branch protection can be cleared while the job is still running. In AWS it can create new long-lived access keys and rewrite a role’s trust policy to "AWS": "*". In Azure it can add federated identity credentials named wfx-ci-… that let the compromised repository sign in later without any stored secret. From 12 November, newer copies sent stolen data through Telegram bots instead of fixed servers, so blocking the known IP addresses is no longer enough, OX Security warns.
Stolen AI keys are not a side issue. As our Fireworks AI and LLMjacking briefing explained, leaked model keys often show up first as an unexpected bill.
Were we hit? A decision tree
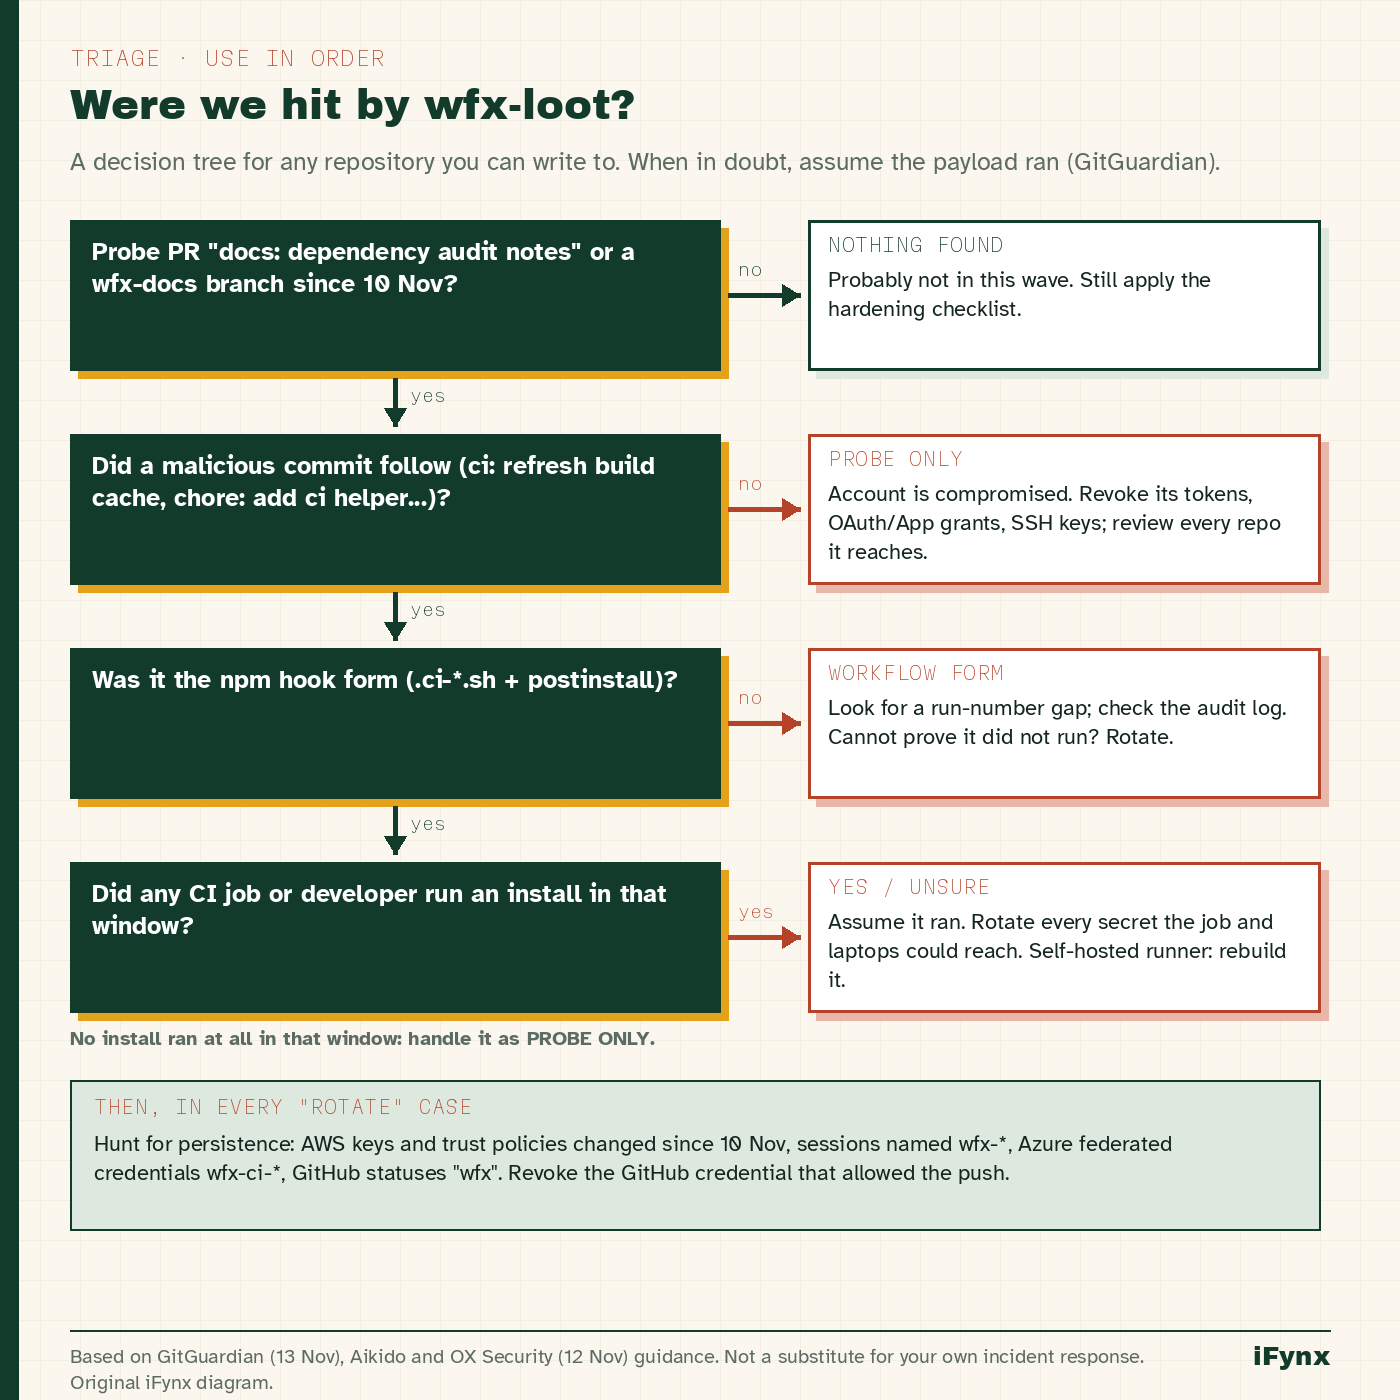
Use this in order. When in doubt, GitGuardian’s advice is to assume the payload ran.
- No probe pull request, no suspicious commits, no run-number gaps since 10 November: you are probably not in this wave. Still do the hardening checklist below.
- Probe only: the account that opened it is compromised. Revoke its personal access tokens, OAuth and GitHub App grants, SSH keys and sessions, and review every other repository that account can reach.
- Malicious commit plus a gap in run numbers (workflow forms): a run was created. Check your organisation audit log to see whether it was approved and executed. If you cannot prove it did not run, rotate.
- npm hook commit plus any install job, or any developer install, in that window: assume it ran. A log line starting
> sh ./.ci-confirms it. Rotate everything the job and those laptops could reach. - Self-hosted runner involved: treat the runner machine as compromised, rebuild it, and rotate the runner’s own credentials and any cloud role attached to the host.
After rotation, hunt for persistence: AWS access keys and role trust policies changed since 10 November and sessions named wfx-*; Azure federated credentials named wfx-ci-*; Google Cloud generateAccessToken and signJwt calls on service accounts; GitHub commit statuses with the description wfx. Then find and revoke the GitHub credential that let the attacker push in the first place, or the next actor will reuse it.
The CI/CD secret checklist for Gulf and Egypt teams
Many teams in the region work in a particular way: agencies and outsourced developers, often in Egypt, are added as collaborators to client repositories in Riyadh, Dubai or Cairo, and a single bot or freelancer account may have write access to a dozen client organisations. That is exactly the path Aikido measured in 10,431 of the probe pull requests. The same pattern showed up in our report on the Cursor breach that started with a key exposed at Fireworks AI: one leaked credential crosses company lines. Here is the checklist we use.
Identity and access
- Kill long-lived personal tokens. Prefer fine-grained tokens with an expiry, limited to named repositories. Where your plan allows, require approval for tokens that reach your organisation, and set an expiry policy.
- Replace bot users with GitHub Apps. A bot account with a password and a classic token is a permanent key. App installation tokens are short-lived and scoped. The WebdriverIO bot account pushed two malicious commits that bypassed branch protection, OX Security reports.
- Time-box collaborator access. Give agencies and contractors access per project, review it monthly, and remove it on handover. Ask your vendors the same question about their own staff.
Pipelines
4. Pin required checks to their source. The stealer forged “success” statuses by name. Where GitHub lets you, set the expected app for each required status check, and do not let any account bypass branch protection.
5. Run installs without lifecycle scripts. Use npm ci --ignore-scripts in CI wherever the build does not need install scripts, and allow-list the few packages that do. GitGuardian’s guidance treats an install run at the repository root without --ignore-scripts as the case where the hidden script ran.
6. Give id-token: write only to deploy jobs, and set permissions: explicitly at the top of every workflow so the default token is read-only.
7. Never ship .git in a build or image. Add .git to .dockerignore, check that your live site does not serve /.git/config, and treat any token that ever sat in a build folder as exposed. This is the route Fly.io described.
8. Use ephemeral runners. A self-hosted runner that is reused across jobs keeps credentials, containers and work folders for the next job, and for the next attacker.
Secrets and cloud
9. Scope OIDC trust tightly. In AWS, Azure and Google Cloud, trust only the specific repository and branch or environment that deploys, never a whole organisation or a wildcard.
10. Keep production secrets out of repository-wide scope. Use protected environments with required reviewers for production deploys, so a build job never holds deploy keys.
11. Give AI provider keys a budget. Separate CI keys per project, spend caps and alerts on OpenAI, Anthropic and Gemini accounts, and a quick way to revoke them.
Detection and response
12. Alert on deleted workflow runs and on unusual pushes to default branches from personal tokens, using the organisation audit log or your security tooling.
13. Write the rotation runbook before you need it. List every secret, who owns it, where it is used and how to rotate it in under an hour. Our FBI ARTEX briefing shows why speed now matters: attackers automate this work.
If personal data was reachable from a stolen key, for example a production database credential, check the breach-notice duties that apply to you in the UAE, Saudi Arabia or Egypt with your legal adviser. Secret leaks on GitHub are not new: our Claude Code secrets report and our MCP server security checklist cover two other routes keys take out of a company.
What is still not known
The sources agree on the method and disagree on totals, which keep rising. Not yet established: how most of the original account credentials were stolen (Fly.io has explained only its own small share); whether the stealer was deployed in private repositories (its code has settings for them); who runs the campaign; and whether the overlap with GhostAction means resold credentials or a shared seller. Aikido notes Indonesian-language comments in newer versions but does not attribute the campaign. GitHub had published no statement, advisory or changelog entry on wfx-loot when we checked on 16 November.
How iFynx can help
We help Gulf and Egypt product teams make sure a stolen token does not become a stolen company.
- CI/CD secret audit and rotation runbook. Our Software Maintenance team reviews your GitHub organisation, tokens, collaborators and workflows, checks for the wfx-loot indicators, and writes a rotation runbook your team can run in under an hour.
- Hardened pipelines. Through API & Backend Engineering, we move deploys to scoped OIDC roles, protected environments, ephemeral runners and script-free installs, without breaking your release flow.
- Checks that stay on. Our Quality Assurance team adds pipeline checks and alerts for deleted runs, new install hooks and workflow changes, so the next campaign is spotted in minutes, not weeks.
Worried a probe reached your repositories? Talk to iFynx, part of our Maintenance & Growth and Software Development services.
Frequently asked questions
What is wfx-loot?
wfx-loot is the name Aikido gave to a CI secret stealer that an attacker pushed into GitHub repositories from 10 November 2026 using stolen credentials of 4,837 GitHub accounts. StepSecurity calls the same campaign WFX Phantom. The script steals GitHub Actions secrets, cloud keys and AI provider keys, then the attacker reverts the commit and deletes the workflow run.
Was GitHub hacked?
No GitHub vulnerability has been reported. The researchers say the attacker used valid stolen tokens that already had write access, and commits appear under real users’ names. Fly.io has explained one route: GitHub App tokens left in a .git/config file that some deployed apps served publicly, affecting a small number of accounts. The source of most tokens is not yet known. GitHub had not published a statement on the campaign when we checked on 16 November 2026.
How do I know if my repository was affected?
Search for pull requests titled docs: dependency audit notes, branches named wfx-docs, and commits such as ci: refresh build cache or chore: add ci helper since 10 November. Then look for a missing workflow run number right after those commits, or a hidden .ci- script run by an npm postinstall hook. A probe alone means the account that opened it is compromised.
Which secrets should I rotate?
If the payload ran, rotate every repository and organisation secret and variable, not only the ones the workflow uses, plus cloud roles, registry tokens and AI provider keys the job or runner could reach. Then check AWS, Azure and Google Cloud for new access keys, changed trust policies and federated credentials named wfx-ci, and revoke the GitHub token that allowed the push.
Does npm ci –ignore-scripts protect against this?
It prevents the npm hook form from running in that job, because the hidden script only runs as an install lifecycle script; that is the form that got past GitHub’s hold on modified workflows. It does not stop the workflow injection forms or a stolen token. Combine it with short-lived tokens, GitHub Apps instead of bot users, pinned required checks and tightly scoped OIDC roles.
Sources and update policy
Aikido, wfx-loot campaign pushes CI secret stealer to tens of thousands of repositories (12 November 2026); GitGuardian, wfx-loot: a CI secret stealer pushed with stolen GitHub credentials (13 November 2026; timeline, npm hook bypass, three-hour commit counts); OX Security (12 November 2026; 8,093 repositories, Telegram switch, WebdriverIO bot); StepSecurity, WFX Phantom (12 November 2026); BleepingComputer (12 November 2026); Fly.io security notice (12 November 2026, addendum 13 November). Times converted to Asia/Gaza (UTC+2) by iFynx. Numbers are as published by each researcher and may keep rising.
We will update this article if GitHub publishes a statement, if researchers confirm how the credentials were stolen, or if victims in the region are confirmed. We do not publish malware code, attacker infrastructure or exploitation steps; see the researchers’ reports for full indicator lists.
Related reading
- Cursor Security Breach: How a Key Exposed at Fireworks AI Led to a Malicious Claude Code Extension, and What Dev Teams Should Check Now
- Claude Code Secrets on GitHub: What Apiiro Found in settings.local.json — A Rotate-First Checklist
- Fireworks AI Data Breach: What Was Exposed (Secrets, Datasets, Model Weights), What LLMjacking Is, and What AI Teams in the Gulf and Egypt Should Rotate Now