ACTIVELY EXPLOITED · APACHE CVE-2026-119618 · CHECKED 07:00 ASIA/GAZA, 19 NOV 2026
Patch Apache now if HTTP/2 is on: CVE-2026-119618 is a critical remote code execution flaw in Apache HTTP Server’s mod_http2 (versions 2.4.55 to 2.4.70). Singapore’s Cyber Security Agency says it is reportedly being exploited and a proof-of-concept is public. The fix is Apache 2.4.71, out since 11 November 2026.
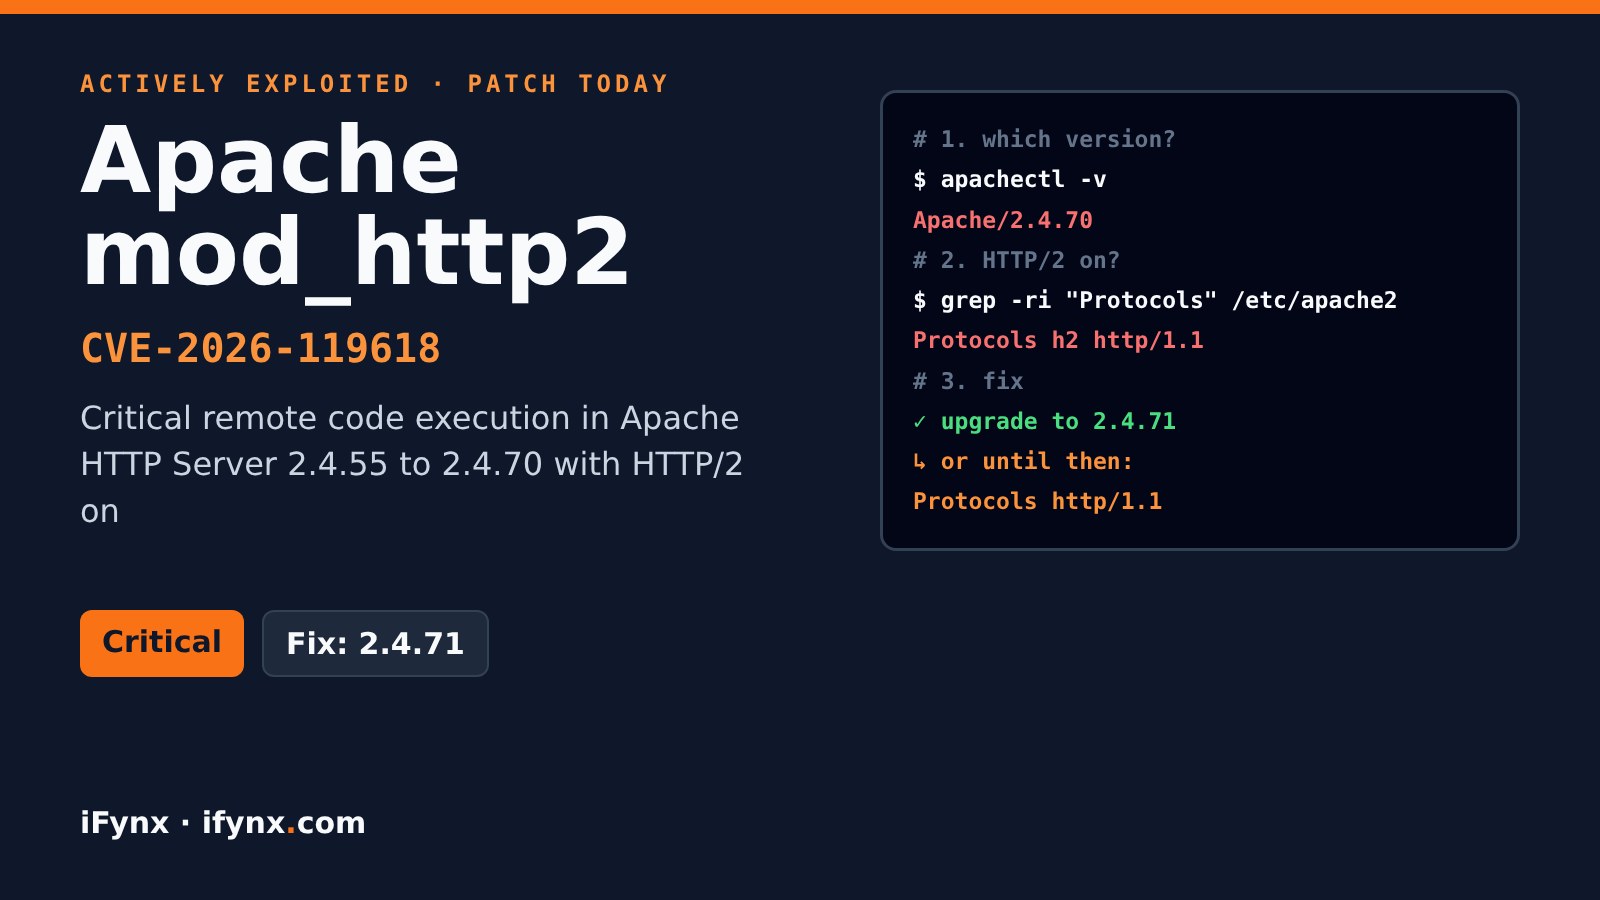
Primary sources: Apache’s security advisory and Singapore CSA alert AL-2026-164. If you cannot upgrade today, switch HTTP/2 off with Protocols http/1.1.
At iFynx we build and host web platforms for banks, fintechs, retailers and government-facing teams in the UAE, Saudi Arabia, Egypt and Palestine, and a large share of the region’s websites still run on Apache, often through cPanel or Plesk. This is the web server patch to do first this week. Below: the facts, a quick way to check, and a patch order. We do not publish exploit details.
Apache mod_http2 flaw: key facts
| Point | What we know |
|---|---|
| CVE | CVE-2026-119618, mod_http2 heap corruption leading to RCE |
| Severity | Apache: Critical. Singapore CSA: CVSS 3.1 8.1 |
| Affected | Apache HTTP Server 2.4.55 to 2.4.70 with mod_http2 enabled; mod_h2 2.0.8 to 2.0.42 |
| Not affected | Servers that only serve HTTP/1.1 |
| Fix | Apache 2.4.71 (11 Nov 2026) or a patched OS package |
| Exploited? | Yes, reportedly, per Singapore CSA on 17 Nov 2026; public proof-of-concept exists |
| Found by | Anthropic’s OSS Scanner (26 Oct) and Google Cloud researchers (3 Nov), per Apache |
| Exposure | Wiz says 64% of cloud environments it examined had affected versions (HTTP/2 not checked) |
Am I affected? Three checks
Checklist (five minutes per server)
httpd -v or apache2 -v. 2.4.55 to 2.4.70 is in range. On Debian, Ubuntu, RHEL and similar, check your vendor’s advisory, because a fixed package can keep an older version number.http2_module and a Protocols line containing h2 or h2c, in every virtual host.Patch order for Gulf and Egypt teams
Protocols http/1.1 everywhere, reload, confirm h2 is goneHosting and control panels: if you rent shared or managed hosting, ask your provider in writing whether its Apache servers are on 2.4.71 or a patched build. cPanel, Plesk and similar panels ship their own Apache packages, so updating the operating system alone may not be enough.
Why this matters in the UAE, Saudi Arabia and Egypt
Government portals, university sites, e-commerce stores and many WordPress sites in the region run on Apache, and HTTP/2 is switched on by default in many TLS setups. A flaw that gives code execution without a login on the web server is the kind of hole ransomware crews and data thieves use first. Under the UAE’s information assurance standards, Saudi Arabia’s NCA controls and Egypt’s Law 151 of 2020, a known, exploited and patchable flaw left open is hard to defend after an incident.
More from this week: Java4Shell: patch order for Gulf and Egypt teams and Was Nvidia hacked? The Gentlemen claim and an edge-device checklist.
How iFynx can help
iFynx builds, hosts and maintains websites and platforms in Arabic and English for the UAE, Saudi Arabia, Egypt and Palestine. We can:
- Find every Apache server you run and check its version and HTTP/2 setting
- Patch or apply the HTTP/1.1 workaround without taking your site down
- Review logs for signs of compromise before the patch
Frequently asked questions
What is CVE-2026-119618?
A critical flaw in mod_http2, the module that gives Apache HTTP Server its HTTP/2 support. A race condition in how it handles request headers can corrupt memory and lead to remote code execution without a login. Apache rates it Critical; Singapore’s Cyber Security Agency gives it CVSS 3.1 score 8.1.
Which Apache versions are affected?
Apache HTTP Server 2.4.55 through 2.4.70 with mod_http2 enabled, and the standalone mod_h2 module 2.0.8 through 2.0.42. Servers that only speak HTTP/1.1 are not exposed. The fix is Apache 2.4.71, released on 11 November 2026, or your Linux vendor’s patched package.
Is it being exploited?
Yes, according to Singapore’s Cyber Security Agency, which said on 17 November 2026 that the flaw is reportedly being actively exploited and that a proof-of-concept exploit is public. We do not publish exploit details.
How do I check if my server uses HTTP/2?
Look for LoadModule http2_module and a Protocols line containing h2 or h2c in your Apache configuration, including every virtual host. Many control panels and default TLS setups turn HTTP/2 on automatically, so check rather than assume.
What if I cannot upgrade today?
Turn HTTP/2 off: set Protocols http/1.1 in the main config and every virtual host, reload Apache, and confirm the server no longer offers h2. Your site keeps working over HTTP/1.1. Then upgrade as soon as you can.
Does this affect WordPress and cPanel sites in the Gulf and Egypt?
It affects the web server, not WordPress itself. Many WordPress, cPanel and Plesk servers in the UAE, Saudi Arabia and Egypt run Apache with HTTP/2 enabled, so check them. Sites behind Nginx-only or LiteSpeed stacks are not affected by this specific bug, but check whether Apache sits behind your proxy.
Sources
- Apache HTTP Server 2.4 vulnerabilities (official advisory, CVE-2026-119618)
- Singapore Cyber Security Agency alert AL-2026-164 (17 Nov 2026)
- Wiz Research: CVE-2026-119618 analysis
- Cyber Security News: Apache HTTP Server RCE actively exploited