LIVING TRACKER · LAST CHECKED 21 NOVEMBER 2026 (ASIA/GAZA)
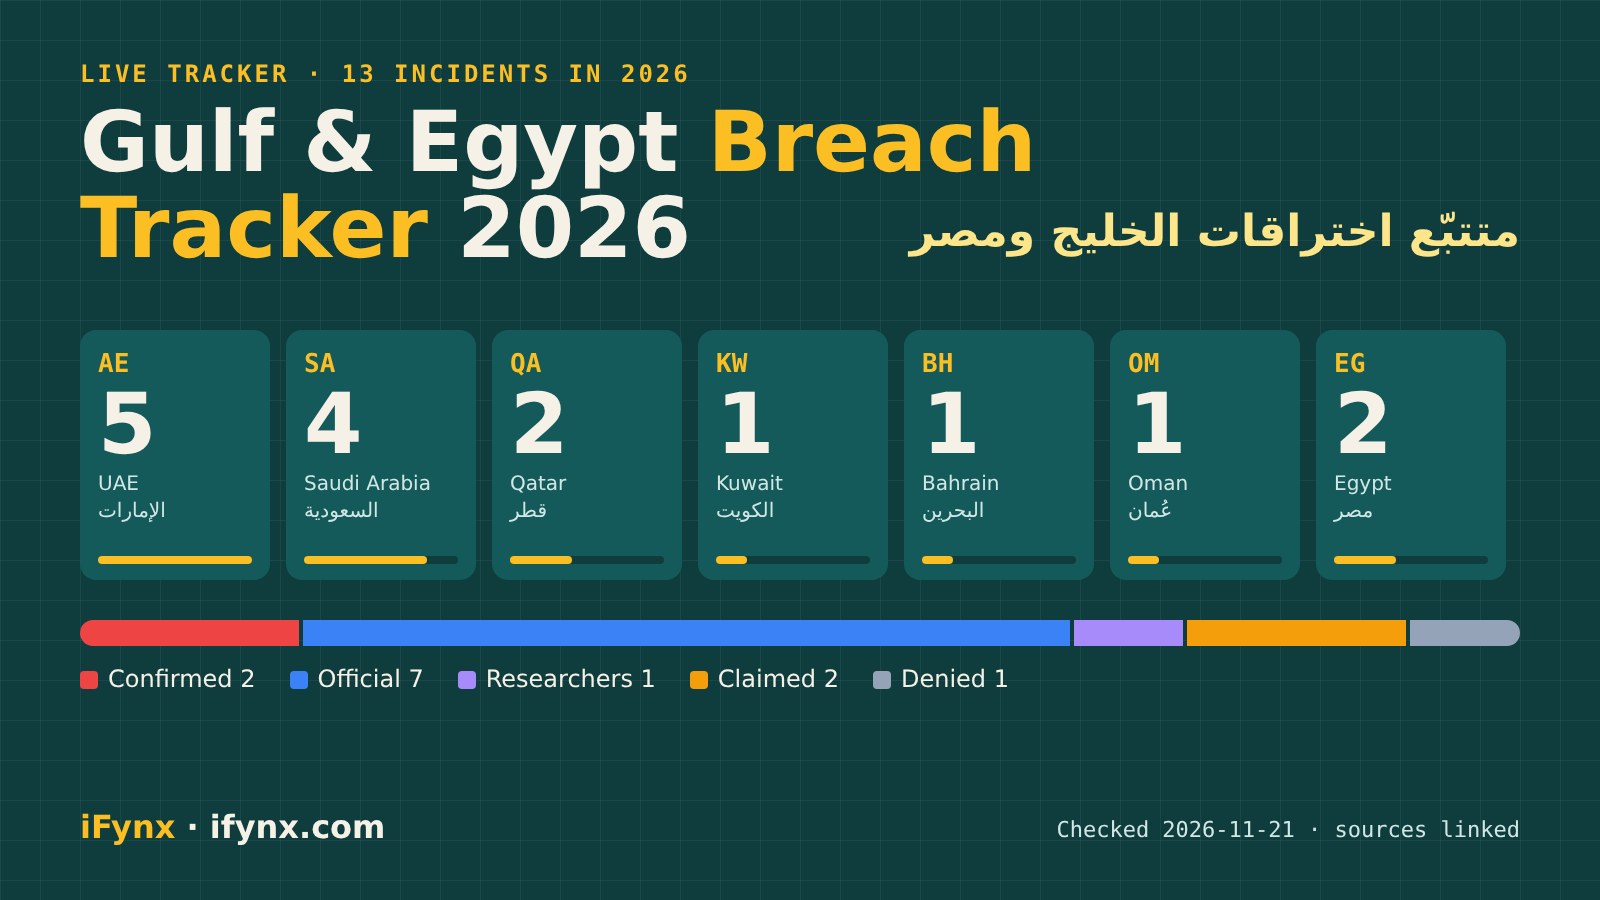
This tracker lists 13 publicly reported cyber incidents in the Gulf and Egypt in 2026, each with its source and a clear status. 2 were confirmed by the organisation hit, 7 come from official statements or regulators, 1 from researchers only, 2 are attacker claims nobody has confirmed, and 1 was denied.
We add new incidents as they are reported and update existing ones when a company, regulator or court says more. Claims are never shown as facts: every row says who said it.
The Gulf and Egypt data breach tracker is a free, sourced list kept by iFynx, a software and product studio that builds apps and platforms for companies in the UAE, Saudi Arabia, Qatar, Kuwait, Bahrain, Oman and Egypt. Most breach lists are global and in English, and they mix confirmed incidents with ransomware gangs’ boasts. This one covers our region only, in Arabic and English, and labels every entry by who actually said it.
How to read this tracker
- Confirmed by the victim the company or agency that was hit confirmed it.
- Official statement a government body, regulator or police said it; the victim may be unnamed.
- Researchers only security researchers published evidence; no victim or government statement yet.
- Attacker claim, unconfirmed only the attackers (or posts) say it happened. Not proven.
- Denied by the victim the organisation named said it did not happen.
Which Gulf countries had the most reported cyber incidents in 2026?
🇦🇪
5
UAE
🇸🇦
4
Saudi Arabia
🇶🇦
2
Qatar
🇰🇼
1
Kuwait
🇧🇭
1
Bahrain
🇴🇲
1
Oman
🇪🇬
2
Egypt
Incidents in 2026 that name each country. A regional item counts for every country it names.
These are reported incidents, not all incidents. Countries where regulators publish decisions and officials speak openly about attacks (the UAE and Qatar, for example) will show more entries than countries where little is disclosed. Read the counts as a picture of disclosure, not of who is safest.
Cyber incidents in the Gulf and Egypt in 2026 (newest first)
6 Oct 2026 · 🇸🇦 Saudi Arabia · Construction
CRCC / Sama Construction consortium (reported World Cup 2034 builder)
Attacker claim, unconfirmed
Monitoring firm Hackmanac reported that a group called WallStreet claims it stole “more than 1.5 million files” (about 17 TB), said to include data on 150,000 employees, after a compromise on 3 October. CRCC had not responded and the National Cybersecurity Council did not comment.
Sources: The National
15 Sep 2026 · 🇦🇪 UAE · Private sector / government supplier
Unnamed private company supporting a UAE government sector
Official statement
The UAE Government’s head of cyber security, Dr Mohamed Al Kuwaiti, said an attacker got in through a vulnerability that had not been patched, demanded “more than $5 million” and threatened to leak the data. The company was not named, and the two newspapers differ on whether any data was actually leaked.
Sources: The National · Gulf News
10 Aug 2026 · 🇦🇪 UAE · Critical sectors
Aviation, energy and education sectors
Official statement
The UAE Cyber Security Council said organised attacks using intrusion attempts, targeting of operational accounts and phishing were “contained before any systems or services could be compromised”. No attacker or figures were given.
Sources: The National
3 Jul 2026 · 🇦🇪 UAE · Banking and finance
UAE financial sector
Official statement
The UAE Cyber Security Council said it foiled a series of “sophisticated cyber attacks” on the financial sector using phishing and malware, with no disruption to services.
Sources: The National
29 Jun 2026 · 🇸🇦 Saudi Arabia · Data protection enforcement
Unnamed entities fined by SDAIA
Official statement
The Saudi Data and AI Authority (SDAIA) announced fines and warnings for entities that broke the Personal Data Protection Law, including failing to report data-leak incidents within 72 hours and marketing without consent. Names and amounts were not given in the report we read.
Sources: Akhbaar24
June 2026 · 🇸🇦 Saudi Arabia · Transport / listed company
Budget Saudi (vehicle leasing)
Confirmed by the victim
In a Saudi Exchange disclosure, the company confirmed “unauthorised access to a limited portion of the data of certain customers through the mobile app”. It said no financial or banking data was affected and that it is investigating with government authorities.
Sources: AGBI
18 May 2026 · 🇪🇬 Egypt 🇦🇪 UAE 🇶🇦 Qatar · Law enforcement
INTERPOL Operation Ramz (13 MENA countries)
Official statement
INTERPOL said police in 13 countries, including Egypt, the UAE and Qatar, arrested “201 individuals”, identified 3,867 victims and seized 53 servers in a phishing, malware and scam crackdown that ran from October 2025 to 28 February 2026.
Sources: INTERPOL
5 May 2026 · 🇴🇲 Oman · Government
Omani government bodies, mainly the Ministry of Justice and Legal Affairs
Researchers only
Researchers at Hunt.io found an exposed attacker server holding scripts and logs pointing to intrusions at up to 12 Omani government bodies, and “over 26,000” Ministry of Justice user records. Hunt.io made no group-level attribution. We found no Omani government statement.
Sources: Hunt.io · Cyber Security News
14 Apr 2026 · 🇸🇦 Saudi Arabia 🇧🇭 Bahrain · Industry / steel
Sulb (Saudi Arabia) and Foulath (Bahrain) steel companies
Attacker claim, unconfirmed
A hacker group calling itself Handala claimed it caused a “complete disruption of operations” at both companies. We found no confirmation from either company. Treat as an unverified claim.
Sources: News.az
5 Mar 2026 · 🇰🇼 Kuwait · Government
Kuwait government digital systems
Official statement
Kuwait’s National Cybersecurity Center said “multiple cyber activities and threats” targeting some of the country’s digital systems were “promptly addressed and contained”, with no service disruption.
Sources: Arab Times
18 Feb 2026 · 🇦🇪 UAE · Events / finance
Abu Dhabi Finance Week (via a third-party vendor)
Confirmed by the victim
A storage system run by a vendor exposed passport and ID scans of attendees without a password. ADFW confirmed “a vulnerability in a third-party vendor-managed storage environment” affecting a “limited subset” of attendees. The Financial Times reported more than 700 documents; ADFW did not confirm that number.
Sources: The National · TechRadar
11 Feb 2026 · 🇪🇬 Egypt · Aviation
EgyptAir
Denied by the victim
Posts claimed data on about 104,000 people, including staff and job applicants, was for sale. EgyptAir said no successful intrusion was detected, and the Cabinet media centre, citing the Ministry of Civil Aviation, said no breach or leak was found.
2 Feb 2026 · 🇶🇦 Qatar · Sports
Unnamed sports company (NCSA binding decision)
Official statement
Qatar’s National Cyber Security Agency issued Binding Decision No. 3 of 2025 after its teams identified a personal data breach at a sports company, finding “inadequate technical, administrative, and physical measures” under the Personal Data Privacy Protection Law. No fine was reported.
Sources: The Peninsula · Qatar Tribune
Landmark breaches before 2026
The older incidents people in the region still search for, with what was actually confirmed.
2025 · 🇦🇪
634 UAE entities named in a claimed Oracle Cloud breach Official statement
The UAE Cyber Security Council said 634 UAE entities were targeted in a global hack claimed by an actor called rose87168. Oracle denied its cloud was breached.
Sources: The National
2025 · 🇦🇪
Bybit (Dubai-based crypto exchange) Confirmed by the victim
About $1.5 billion in ether was stolen from a cold wallet. The FBI attributed it to North Korea’s TraderTraitor (Lazarus) hackers.
Sources: TechTarget
2023 · 🇪🇬
Fawry (payments) Denied by the victim
An outage followed a LockBit ransomware claim. Fawry denied any attack or data breach, while a bank partner said Fawry was under attack.
Sources: The National
2023 · 🇰🇼
Kuwait Ministry of Finance Confirmed by the victim
The ministry confirmed a ransomware attack and isolated systems; the Rhysida gang listed it as a victim. Payroll ran on a separate network.
Sources: The Record
2021 · 🇸🇦
Saudi Aramco (data held by contractors) Confirmed by the victim
Aramco confirmed an “indirect release” of limited data held by third-party contractors, said its own systems were not breached; an extortionist demanded $50 million.
Sources: The National
2018 · 🇦🇪
Careem (ride-hailing) Confirmed by the victim
Careem confirmed that 14 million customers and captains had names, emails, phone numbers and trip data accessed; no evidence passwords or card numbers were taken.
Sources: Khaleej Times
2016 · 🇶🇦
Qatar National Bank Attacker claim, unconfirmed
A 1.4GB file said to be QNB customer data was posted online. The bank investigated, did not confirm the data and said there was no financial impact.
Sources: MEED
2012 · 🇸🇦
Saudi Aramco (Shamoon wiper) Confirmed by the victim
Aramco confirmed malware hit about 30,000 workstations; oil production was not affected. It remains the region’s best-known destructive attack.
Sources: Threatpost
What the 2026 record shows
- Suppliers are the soft spot. The Abu Dhabi Finance Week exposure came from a vendor’s storage, and the unnamed UAE company that faced a $5 million demand was a supplier to a government sector. Aramco’s 2021 leak also came from contractors. Your security is only as good as the companies holding your data.
- Unpatched software is still how attackers get in. UAE officials said the $5 million case started with a vulnerability that had not been patched.
- Mobile apps hold customer data too. Budget Saudi’s confirmed leak came through its mobile app, not its core systems.
- Regulators are now acting. Qatar’s NCSA issued a binding decision after a breach, and SDAIA fined entities in Saudi Arabia for, among other things, not reporting data leaks within 72 hours.
- Many headlines are claims. Several 2026 stories rest only on attacker posts, and one was firmly denied. Check the status before you share.
Checklist for Gulf and Egypt companies
How we verify each entry
An incident is added only when a named news outlet, regulator, police body, company disclosure or security research team has published it, and we link that source. We do not list victims from ransomware leak sites alone. We quote numbers exactly as the source gives them and say who gave them. We do not attribute attacks to countries ourselves; where an official agency (for example the FBI) has made an attribution, we report it as theirs. If you represent an organisation listed here and have an update or correction, contact iFynx and we will review it.
How iFynx can help
iFynx designs and builds web platforms and mobile apps for Gulf and Egypt companies, with security built in from the first sprint instead of added after an incident.
- Security review of an existing app or website: API access control, exposed storage, admin panels and dependencies.
- Building privacy into new products: data minimisation, ID-document handling and PDPL-ready consent flows.
- Hardening your vendor setup: what data each supplier gets, and how to take it back.
- Fixed-price or monthly plans; see typical ranges with our app cost calculator.
Frequently asked questions
What is the Gulf and Egypt data breach tracker?
A free list by iFynx of publicly reported cyber incidents in the UAE, Saudi Arabia, Qatar, Kuwait, Bahrain, Oman and Egypt. Each entry has a date, the organisation, a status label and links to its sources. It was last checked on 21 November 2026.
How many data breaches were reported in the Gulf and Egypt in 2026?
This tracker lists 13 incidents so far in 2026. 2 were confirmed by the organisation affected, 7 come from official statements, and the rest are researcher reports, unconfirmed claims or denials. Many incidents are never disclosed, so the real number is higher.
Why are some incidents marked as claims?
Ransomware and hacker groups often announce victims to put pressure on them, and some claims are exaggerated or false. We show a claim only when a named outlet or research firm reported it, and we label it clearly until the organisation or an official confirms or denies it.
Do companies in Saudi Arabia have to report data breaches?
Yes. Under Saudi Arabia’s Personal Data Protection Law, a data leak must be notified to SDAIA within 72 hours, and in 2026 SDAIA fined entities that failed to do so. Read our PDPL guide for details.
How can my company avoid becoming an entry in this tracker?
Patch internet-facing systems quickly, control what data your vendors hold, test your app’s API for access-control flaws, train staff against phishing and keep a breach response plan ready. iFynx can review your app or website and fix what it finds.
Related reading
- Saudi PDPL compliance in 2026
- UAE online fraud: the government-impersonation scam
- Infoblox breach: how a vendor became the way in
Every Sunday: the most serious confirmed CVEs and breaches, who is exposed in Saudi Arabia, the UAE and Egypt, and what to patch first. Free, in English and Arabic, one-click unsubscribe.
✓ You’re subscribed. A welcome email is on its way; the first issue arrives on Sunday.