SUPPLY-CHAIN ATTACK · MICROSOFT AGENT-FRAMEWORK · CHECKED 09:00 ASIA/GAZA, 19 NOV 2026
If your team builds AI agents in Python, check now: Microsoft’s agent-framework package on PyPI shipped two malicious versions, 1.26.1 and 1.26.2, on 17 November 2026. They stole Azure, Azure DevOps, GitHub and other secrets the moment Python started. They were online for about an hour. The safe version is 1.26.0.
Sources: Wiz Research and Socket. If either version was installed anywhere, rebuild and rotate every secret that machine could reach.
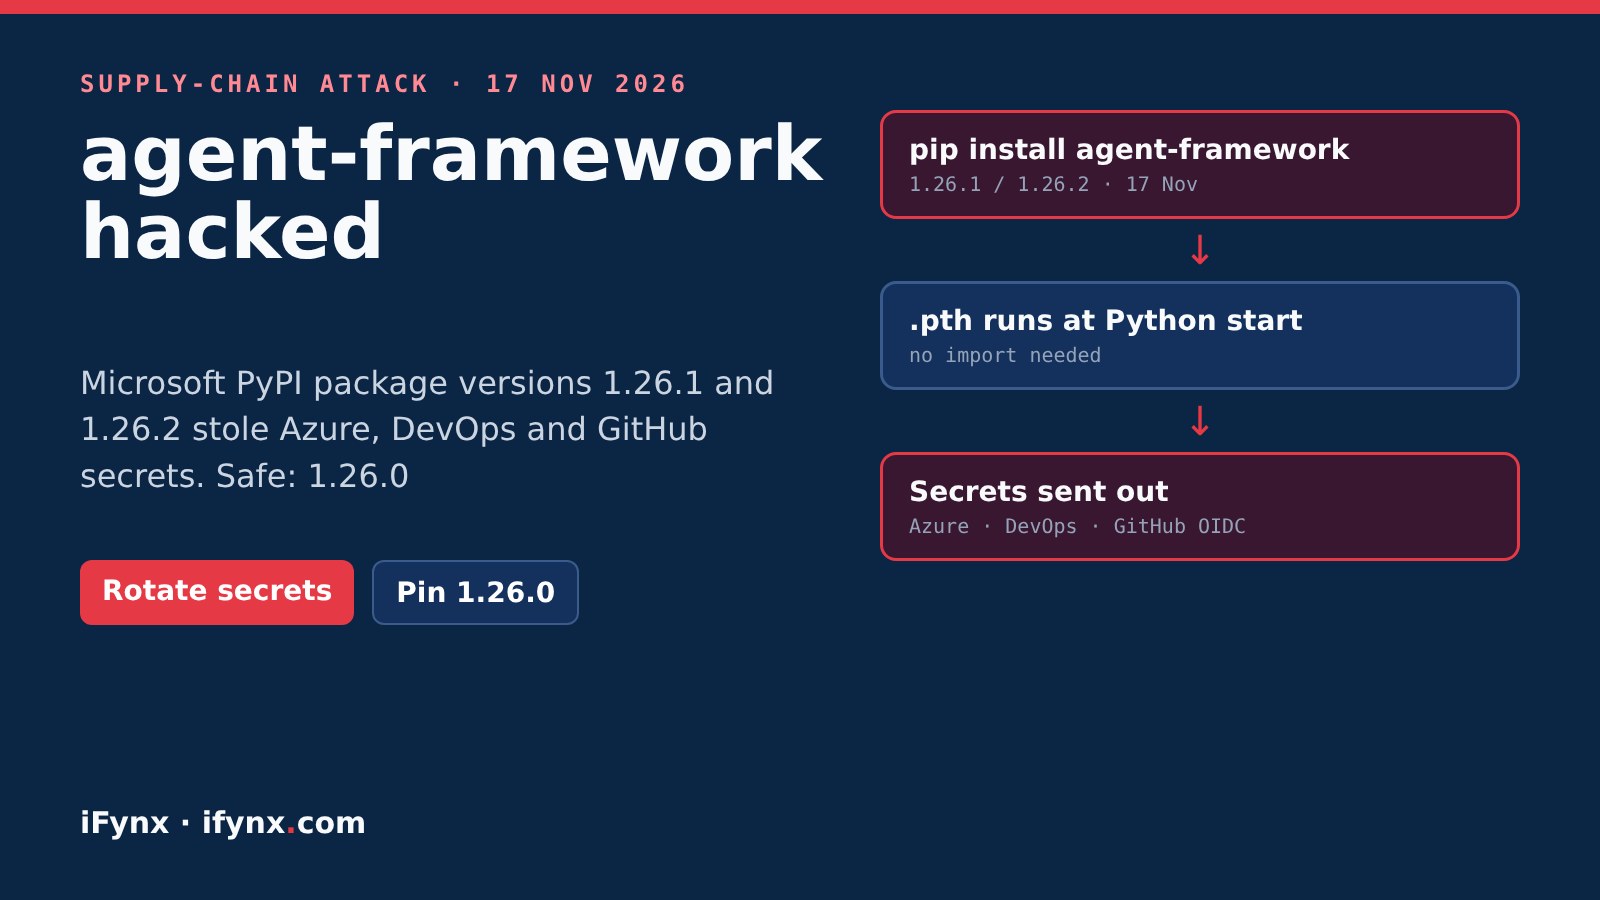
At iFynx we build AI and web platforms for banks, fintechs and government-facing teams in the UAE, Saudi Arabia, Egypt and Palestine, and many of those teams build on Azure and Microsoft’s AI tooling. This attack hit exactly that stack, through a package with Microsoft’s own name on it. Below: what happened, how to tell if you were exposed, and what to rotate.
agent-framework compromise: key facts
| Point | What we know |
|---|---|
| Package | agent-framework on PyPI (Microsoft Agent Framework, Python) |
| Bad versions | 1.26.1 (about 20:35 UTC) and 1.26.2 (about 21:08 UTC), 17 Nov 2026 |
| Removed | Both gone from PyPI by 21:30 UTC |
| Safe version | 1.26.0 (12 Nov 2026) |
| How it ran | A .pth file that Python runs at every start, even without importing the package |
| Steals | Env secrets, other processes’ secrets, pip/npm/git/Docker/Hugging Face/Azure files, Azure and Azure DevOps tokens, GitHub OIDC (1.26.2) |
| How published | Attacker appears to have had a key for Microsoft’s ESRP publishing service (Wiz) |
| Victims seen | Three unique successful exfiltrations counted by Wiz on the capped endpoint |
Were you exposed? Quick checks
Exposure checklist
pip show agent-framework in every environment, and search lockfiles and CI logs for agent-framework==1.26.1 or 1.26.2.agent_framework_meta.pth or af_runtime_diag.pth.webhook.site from build servers or developer machines on 17-18 November.pip install agent-framework without a version between 20:35 and 21:30 UTC on 17 November may have pulled a bad version.What to do if you find it
Removing the package is not enough. The secrets were sent out the moment Python started. Uninstalling or upgrading does not take them back, so rotation is the real fix. Do the rotation from a clean machine, not the affected one.
Why this matters in the UAE, Saudi Arabia and Egypt
Banks, telecoms and government teams in the region are building AI agents fast, often on Azure with Microsoft’s own SDKs, and CI runners usually hold the keys to cloud subscriptions. This is the second big CI secret-stealing attack we have covered this week, after wfx-loot: GitHub Actions malware stealing CI secrets. The pattern is the same: trust in a known publisher, automatic installs, and secrets left in environment variables. Short-lived credentials, pinned dependencies and a short delay before new versions reach production would have blunted this one.
How iFynx can help
iFynx builds AI and web platforms in Arabic and English for the UAE, Saudi Arabia, Egypt and Palestine. We can:
- Search your repos, CI and images for the bad versions
- Plan and run the secret rotation across Azure, Azure DevOps and GitHub
- Harden your Python and Node supply chain with pinning, hashes and release delays
Frequently asked questions
What happened to Microsoft’s agent-framework package?
On 17 November 2026 two malicious versions of agent-framework, Microsoft’s Python package for building AI agents, were published to PyPI: 1.26.1 at about 20:35 UTC and 1.26.2 at about 21:08 UTC. Both were gone by 21:30 UTC. They contained a credential stealer. The last safe version is 1.26.0.
How did attackers publish under Microsoft’s name?
According to Wiz, the attacker appears to have obtained a certificate and private key for Microsoft’s internal signing and publishing service (ESRP). How those were obtained is not known yet, and Microsoft has not published a statement we could find.
What does the malware steal?
Secrets in environment variables (tokens, keys, AWS, Azure, GitHub, OpenAI and similar), secrets from other running processes, credential files for pip, npm, git, Docker, Hugging Face and Azure, Azure managed-identity and Azure DevOps tokens, and in 1.26.2 GitHub Actions OIDC tokens. It sends them to a webhook.site address.
I never imported the package. Am I safe?
Not necessarily. The malicious versions drop a .pth file that Python runs on every start, so simply having 1.26.1 or 1.26.2 installed in an environment was enough for the stealer to run.
How many victims are there?
Wiz looked at the attacker’s collection endpoint, which was on a free plan capped at 100 requests, and counted three unique successful thefts of victim data among 50 requests. That is a lower bound for what that endpoint captured, not a full count of everyone who installed it.
What should teams in the Gulf and Egypt do now?
Search lockfiles, CI logs, virtual environments and container images for agent-framework 1.26.1 or 1.26.2. If found, rebuild from a clean image pinned to 1.26.0 and rotate every secret that environment could reach, especially Azure, Azure DevOps and GitHub. iFynx can help with the search and rotation.
Sources
- Wiz Research: malicious version of Microsoft’s Agent Framework published to PyPI (17 Nov 2026)
- Socket: agent-framework PyPI package compromised with credential stealer (17 Nov 2026)
- Cyber Security News: Microsoft’s Agent Framework PyPI package hacked