ISSUE #1 · WEEK OF 15-21 NOV 2026 · CHECKED 08:00 ASIA/GAZA, 22 NOV
Patch VMware vCenter and Cisco Expressway first: both are being exploited and CISA added both to its Known Exploited Vulnerabilities list on 20 November 2026. Then Apache HTTP Server (mod_http2), nginx and Java, which all got critical fixes this week.
Below: seven items in patch order, three breaches to know about, one Windows flaw to watch, and a Monday checklist. Sources are linked on every item.
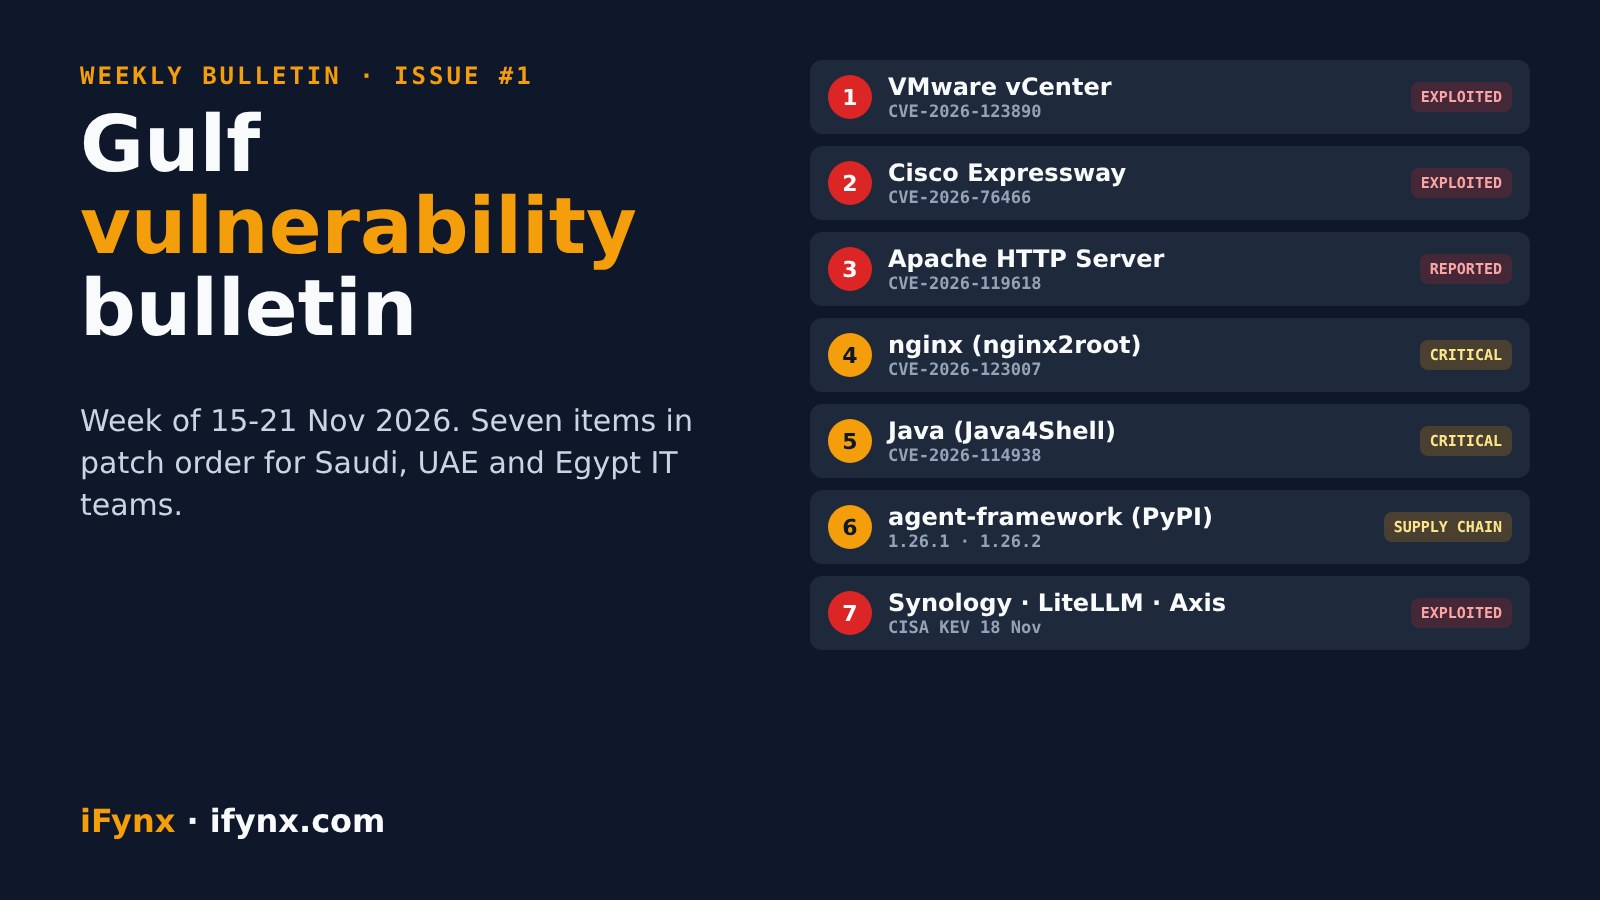
This is the first weekly vulnerability bulletin from iFynx, written for IT managers, developers and owners at companies in Saudi Arabia, the UAE, the wider Gulf and Egypt. Every Sunday we read the vendor advisories, CISA’s Known Exploited Vulnerabilities catalogue and breach reports, keep only what is confirmed, and put it in the order we would patch it for our own clients. We never publish exploit code.
What should I patch first this week?
| # | Product | Status | Action |
|---|---|---|---|
| 1 | VMware vCenter | EXPLOITED · CISA KEV | Update to 9. |
| 2 | Cisco Expressway | EXPLOITED · CISA KEV | Apply the fixed release in Cisco’s advisory; clustered deployments are the ones affected. |
| 3 | Apache HTTP Server | REPORTED EXPLOITED | Upgrade to 2. |
| 4 | nginx (nginx2root) | CRITICAL · NO ATTACKS YET | Update to 1. |
| 5 | OpenJDK / Java (Java4Shell) | CRITICAL · NO ATTACKS YET | Install the 17 Nov OpenJDK/Oracle updates. |
| 6 | Microsoft agent-framework (PyPI) | SUPPLY CHAIN | Pin 1. |
| 7 | Synology DSM, LiteLLM, Apache Axis 1.x | EXPLOITED · CISA KEV | Synology: DSM 7. |
The seven items, with sources
#1 · EXPLOITED · CISA KEV
VMware vCenter: CVE-2026-123890 (CVSS 9.8)
Authentication bypass in the control room of your virtual servers. Mandiant ties exploitation since early September to a China-nexus group; CISA added it to KEV on 20 Nov.
Do this: Update to 9.1.1.0200, 9.0.2.0200 or 8.0 U3m. vCenter 7.0 has no public fix.
Sources: Broadcom VMSA-2026-0009 · Security Affairs (KEV) Full iFynx guide →
#2 · EXPLOITED · CISA KEV
Cisco Expressway: CVE-2026-76466 (CVSS 9.8)
Hard-coded credentials in clustered Expressway, the gateway many banks, ministries and hospitals use for video calls. CISA added it to KEV on 20 Nov; F6 reported exploitation after a public proof of concept.
Do this: Apply the fixed release in Cisco’s advisory; clustered deployments are the ones affected.
Sources: Security Affairs (KEV)
#3 · REPORTED EXPLOITED
Apache HTTP Server: CVE-2026-119618 (mod_http2)
Remote code execution in versions 2.4.55 to 2.4.70 with HTTP/2 on. Singapore CSA says it is reportedly exploited. Common under cPanel and Plesk hosting in the region.
Do this: Upgrade to 2.4.71, or turn HTTP/2 off (Protocols http/1.1) until you can.
Sources: Apache advisory · Singapore CSA AL-2026-164 Full iFynx guide →
#4 · CRITICAL · NO ATTACKS YET
nginx (nginx2root): CVE-2026-123007 + 4 more
Five memory-safety bugs fixed on 18 Nov, the worst an HTTP/2 remote code execution. No attacks reported, but the researchers say they hold working exploits. Check Kubernetes ingress and container images too.
Do this: Update to 1.30.7 (stable) or 1.31.9 (mainline) and restart fully; a reload is not enough.
Sources: nginx.org advisories Full iFynx guide →
#5 · CRITICAL · NO ATTACKS YET
OpenJDK / Java (Java4Shell): CVE-2026-114938 (CVSS 9.2)
Base64 decoder memory bug on AVX-512 x86-64 servers that can lead to code execution in Jira, Confluence, Jenkins, Keycloak and Elasticsearch.
Do this: Install the 17 Nov OpenJDK/Oracle updates. Stopgap: -XX:-UseBASE64Intrinsics.
Sources: Oracle CPU Nov 2026 · Calif.io Full iFynx guide →
#6 · SUPPLY CHAIN
Microsoft agent-framework (PyPI): versions 1.26.1 and 1.26.2
Two malicious releases on 17 Nov stole Azure, Azure DevOps and GitHub secrets as soon as Python started. Online for about an hour.
Do this: Pin 1.26.0. If a bad version ran anywhere, rebuild that machine and rotate every secret it could reach.
Sources: Wiz Research · Socket Full iFynx guide →
#7 · EXPLOITED · CISA KEV
Synology DSM, LiteLLM, Apache Axis 1.x: CVE-2024-10441 · CVE-2026-40217 · CVE-2026-90436
Added to KEV on 18 Nov. Synology NAS boxes in small offices, LiteLLM gateways in AI teams, and old Axis 1.x SOAP services in banking middleware.
Do this: Synology: DSM 7.2.2-72806-1 or your branch’s fixed build. LiteLLM: apply the vendor fix and lock down guardrail testing. Axis 1.x: no fix coming, migrate.
Sources: GBHackers (KEV)
Also added to CISA’s list on 20 November: SAP NetWeaver Enterprise Portal CVE-2025-42884 and Apache Roller CVE-2026-129448 (versions 4.0.0 to 6.1.4). Source: Security Affairs.
Breaches this week
- Infoblox (confirmed, 16 Nov): attackers took internal files through a hacked data-migration vendor; reports say some customers’ NIOS configuration snapshots were included. Our guide.
- N-able Mail Assure and SpamExperts (confirmed, 19 Nov): one hosted cloud server was accessed; N-able says it has no evidence customer data was compromised, and the portal and API stayed disabled as a precaution. Source: The Hacker News.
- Nvidia (unconfirmed): a ransomware group’s claim that is still not verified. What we know.
Every confirmed breach in the region is logged in the iFynx Gulf and Egypt data breach tracker.
Windows flaw to watch: FastUnlock
On 19 November a researcher known as Chaotic Eclipse published “FastUnlock”, which he says abuses Narrator to run code from the Windows lock screen on Windows 11 with the November 2026 updates. It needs someone at the device, no fix was stated, and Microsoft had not commented in the reports we checked. For now: keep BitLocker on, do not leave laptops unattended, and watch for Microsoft guidance. Source: Security Affairs.
Monday checklist for Gulf and Egypt IT teams
- List every vCenter and Expressway you run (including disaster-recovery sites) and patch them today.
- Check web servers: Apache version and HTTP/2, nginx version in servers, containers and ingress.
- Find Java runtimes behind Jira, Confluence, Jenkins and Keycloak and update them.
- Search lock files and build logs for agent-framework 1.26.1 or 1.26.2.
- Update Synology NAS boxes and any LiteLLM gateway; plan the exit from Axis 1.x.
- If you use Infoblox or N-able mail filtering, ask your vendor for a written status.
Every Sunday: the most serious confirmed CVEs and breaches, who is exposed in Saudi Arabia, the UAE and Egypt, and what to patch first. Free, in English and Arabic, one-click unsubscribe.
✓ You’re subscribed. A welcome email is on its way; the first issue arrives on Sunday.
How iFynx can help
iFynx builds and runs bilingual web and mobile platforms for companies in the UAE, Saudi Arabia, Egypt and Palestine. If an item in this bulletin touches your stack, we can find where it runs, patch it with minimal downtime and harden what is around it.
Frequently asked questions
Which vulnerability should Gulf and Egypt companies patch first this week?
VMware vCenter CVE-2026-123890. It is critical, it has been exploited since early September, and CISA added it to its Known Exploited Vulnerabilities catalogue on 20 November 2026. Fixed builds are 9.1.1.0200, 9.0.2.0200 and 8.0 U3m.
Is the nginx2root flaw being exploited?
Not as of 22 November 2026. No attacks were reported, but the researchers say they have working exploits, so update to nginx 1.30.7 or 1.31.9 and restart fully.
Is there a fix for the FastUnlock Windows lock-screen flaw?
Not stated as of this issue. The researcher’s claim covers Windows 11 with the November 2026 updates; Microsoft had not published guidance in the reports we checked.
How do I get this bulletin every Sunday?
Subscribe free with the form on this page. The iFynx bulletin arrives every Sunday in English or Arabic, and every email has a one-click unsubscribe link.